Solutions / AI Security

Think Like an AI Attacker. Move at AI Speed.

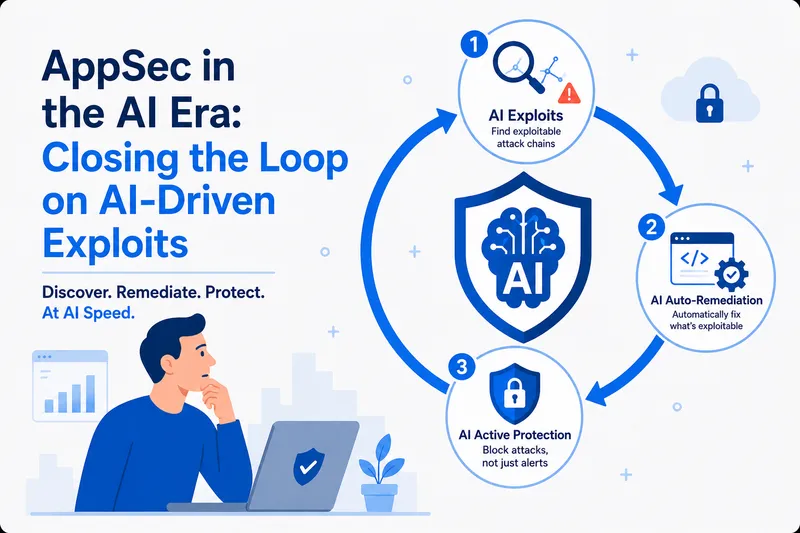
AI finds and chains flaws faster than teams can patch them. Data Theorem's closed-loop AI security: AI Exploits discovers the chains, the AppSec Agent helps you triage them, AI Auto-Remediation drives the fix into your code, and AI Active Protection blocks the chain at runtime until the fix ships.

The Problem

AI Changed Who Finds Your Flaws First.

Attackers now use AI to decompile apps, map APIs and test ideas at machine speed. The issues they look for are rarely critical on their own. They are small ones that line up.

AI-assisted reverse engineering
AI tooling reads decompiled code and hooks running apps faster than any human attacker could.
Faster than the patch cycle
Exploits move in hours. Fixes move through tickets, reviews and release trains.
Discover / AI Exploits

Three Low Findings. One Critical Chain.

Scanners grade every issue on its own. AI Exploits reads the whole field and finds the few that line up into a path to your data.

Low Debug symbols
+
Low API route in strings
+
Low Pinning gap
+
Medium Missing authorization
Critical Customer data exposed
High Medium Low
Your queue says fix the highs. The real path ran through the lows.
How AI Exploits Works

Meet ARCANE, the AI Exploit Engine.

Chains like that one are found by ARCANE, short for AI-analysis of Runtime Code Across Native Environments, our AI exploit engine, which proves every chain at runtime before it reaches you.

Step 1 of 5 Your app, API or source goes in Send the app binary or point at the API. No source code needed, though ARCANE can start from source too, for languages like Python and JavaScript.
Step 2 of 5 Reverse engineered ARCANE decompiles the binary back into readable code, so it sees the app the way an attacker would. An AI reducer then cuts it down to what the model needs.
Step 3 of 5 AI finds the exploit chains AI reads the code and hunts for findings that link into one attack path, the way an AI attacker would.
Step 4 of 5 Verified at runtime Every chain is proven against the running app or API before it reaches you. No guesses in your queue.
Step 5 of 5 A new check for the engine The proven exploit becomes a deterministic check. AI finds it once, and the scanner catches it on every release after.
AppSec Agent Live
How many critical findings do I have?
4 critical across your apps and APIs. One is an AI Exploits chain on checkout. Start there.
Critical 4 High 11 AI Exploit 1
Anything from runtime protection this week?
Mobile Protect blocked tampering attempts on the checkout app, most of them from one cluster of rooted devices.
Mobile Protect Blocked
How do I send findings to our ticketing system?
Open Integrations in the portal, pick your ticketing tool and choose which severities open tickets. Want me to walk you through it?
Triage / AppSec Agent

Ask What Matters. Get a Straight Answer.

The AppSec Agent sits inside the portal and answers in plain language. Ask how many issues you have, what changed, what runtime protection saw this week or where a setting lives.

Findings and counts
Issues by app, API, severity or exploit chain
Runtime events
What was detected and blocked, and where
What to fix first
The chains and criticals that matter now
Help in the portal
Setup, integrations and how-to questions
Fix / AI Auto-Remediation

Found in the App. Fixed in the Code.

Code SAST Secure traces the exploit to the line that caused it and hands your coding agent the exact fix.

  1. Found in the app AI Exploits proves the exploit in the running app or API.
  2. Traced to the code Code SAST Secure finds the exact line that caused it.
  3. Fixed by your agent Your coding agent gets the remediation brief and makes the fix itself.
  4. Verified closed AI Exploits replays the attack. If it no longer works, the finding closes.
AI Exploits, in Mobile Secure or API Secure
AI Exploit Critical
Endpoint skips object-level authorization
GET /orders/{id} on checkout-api
Code SAST Secure
checkout-api/
api/
orders.pyline 42
payments.py
SAST+ ties the runtime finding to this line
Claude CodeCursorGitHub CopilotVS Code Your coding agent Working Done
Remediation brief received from Data Theorem
Editing api/orders.py
42 - return get_order(order_id)
42 + return get_order(order_id, owner=user)
Running the provided test Passed
Pull request opened. Merged automatically, or held for your reviewer.
Finding Missing authorization check Open Closed
Rescan passed AI Exploits replayed the attack. It no longer works.
A deterministic check now guards it on every release
Token Spend

Fewer Tokens. Faster Fixes. Same Agent.

Left alone, an agent has to hunt for the issue, research it, draft, test and try again, and it needs a large model to do it. Data Theorem hands it an optimized remediation brief instead, so your agent spends its tokens on the change, not the investigation.

Without guidance Your coding agent Working Done
Large reasoning model Needed to find and reason about the issue Tokens used
Searching the codebase for the pattern grep, open, read, repeat
Two runs, two different answers no harness, so results vary
Researching the weakness CWE-639, framework docs
Draft failed its test, iterating draft 1 rejected
Pull request opened finally
With Data Theorem guidance Your coding agent Working Done
Small, fast model Enough to apply a known fix Tokens used
Remediation brief Critical
Missing authorization check orders.py:42
1 Scope the lookup to the user
2 Return 403 for anyone else
3 Run the provided test
Applying the fix, test passed scoped to the signed-in user
Pull request opened rescan closes the finding
Illustrative session. Token use depends on your model, your codebase and the finding.
Your models, already approved No added variable cost Less spend per fix
Defend / AI Active Protection

Break the Chain While the Fix Ships.

AI Active Protection watches your app and API as they run. When an exploit is found, it blocks the attack at runtime and keeps blocking until the fix is live.

Mobile Protect Blocks hooking, AI-assisted decompiling and tampering on the device, before the attacker can read your code.
API Secure Spots the abnormal traffic and has your WAF block that client until the fix ships. One targeted rule, no change to your app.
Exposed until the first block, not the next release. Covers the fix however it gets made, then stays on as a backstop.
Exposed Protected at runtime Fix shipped
AI Security

See the Loop on Your Own App

Send one app or one API. See the chains ARCANE proves, how the AppSec Agent ranks them, the fix your agent gets and the block that holds in the meantime.

  • A scoped proof of concept Run on your own app or API, time-boxed and agreed up front.
  • Start from a binary or an API No source code needed to see your first exploit chains.
  • Fixes through your own agent Connect Code SAST Secure and watch remediation land where developers work.