Security in Every Stage, From Code to Runtime
Data Theorem runs inside your software development lifecycle (SDLC), from the first line of code to the apps and APIs running in production. Security keeps pace with every release, and every finding lands where your teams already work.
 Fix sent to your coding agent
 Every pull request checked before merge

 AI Exploits connects the findings

 Every new store version, automatically
 Blocked in the app and at the firewall


 One finding, linked in every tool
Security Can’t Be the Gate at the End Anymore
Coding agents and frequent releases push more code through the pipeline than a manual review at the end can keep up with. Data Theorem was built from day one to run inside the release process instead, so security moves at the speed your teams ship.
- 2013 Founded to automate application security testing, with no manual step in the loop
- Every Release Tested automatically as it is submitted, end to end
- #1 Cloud Native Apps use case, 2025 Gartner® Critical Capabilities for Application Security Testing
Gartner, Critical Capabilities for Application Security Testing, 2025. GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates and is used herein with permission. All rights reserved. Gartner does not endorse any vendor, product or service depicted in its research publications.
Across the Lifecycle
Where Data Theorem Plugs In
Data Theorem plays at every stage. It takes the active role in three: it remediates in the code, runs the security testing between build and release, and monitors and protects your apps and APIs in production. Everywhere else it works through the tools your teams already run.
Code
Issues fixed where developers and agents write code
-
 No bad commits Code SAST Secure
- Findings in the IDE and agent MCP server and CLI
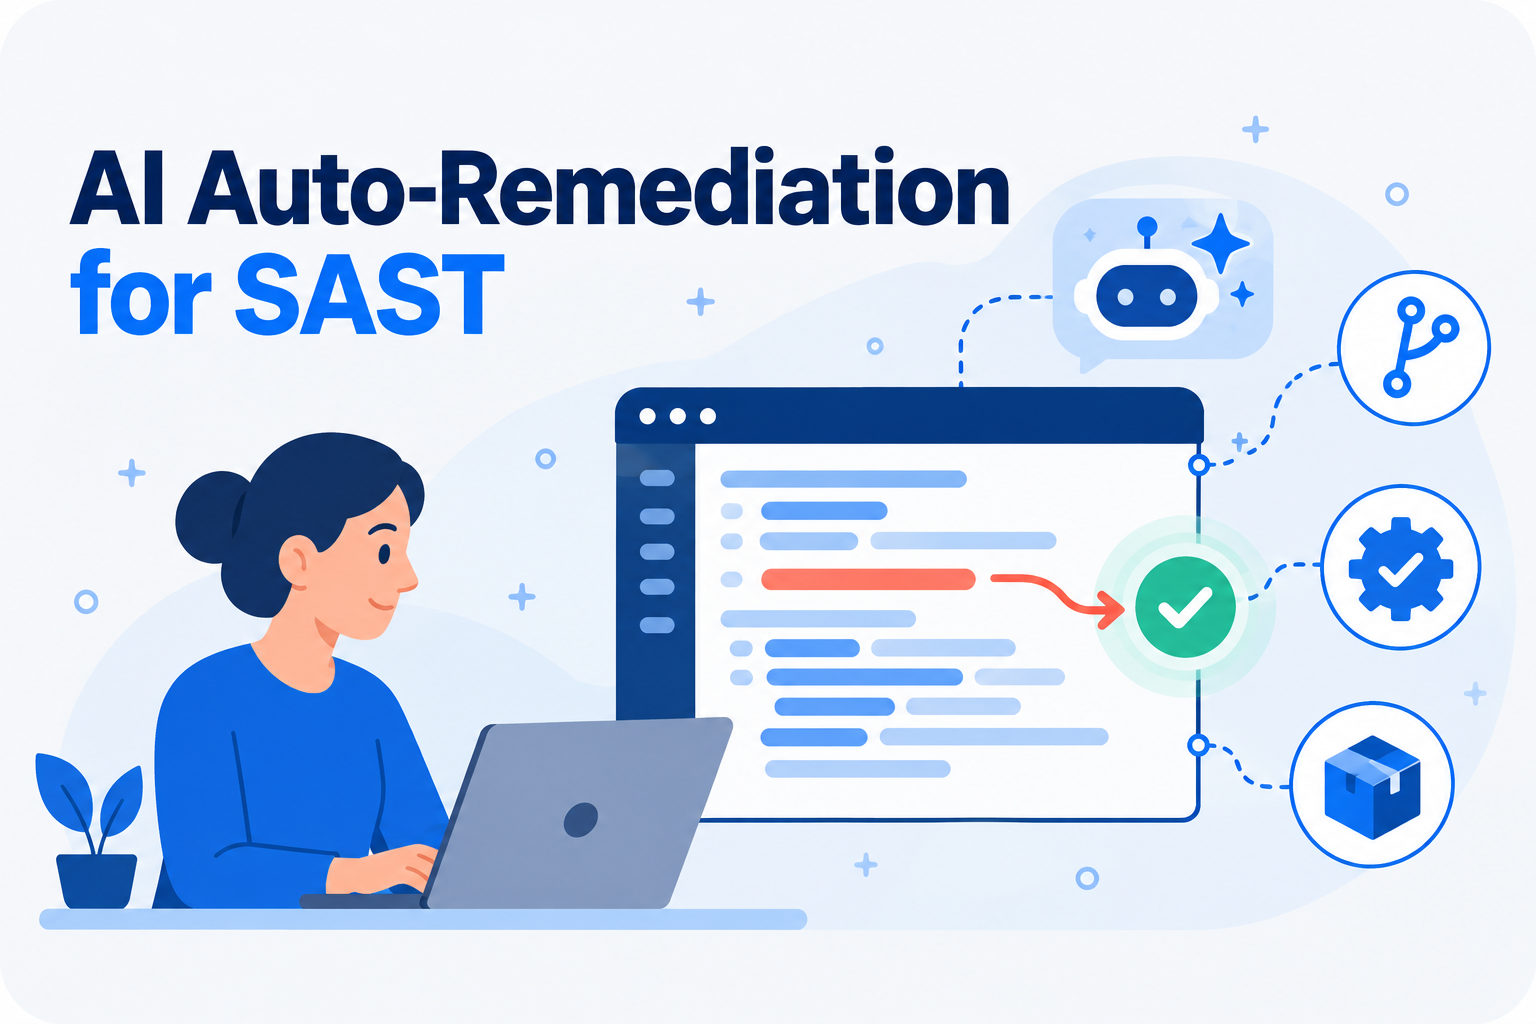
 AI Auto-Remediation


Build
Repos and pipelines, checked on every pull request and build



 AI Governance


Security Testing
Every build tested in your pipeline
- Mobile apps Mobile Secure
- APIs API Secure
- Code Code SAST Secure
AI Exploits 
Release
Store submissions and every published app


Monitor
Apps and APIs monitored and protected in production
-
 In the app Mobile Protect
- At the API API Secure
-
 In the cloud Cloud Secure
AI Active Protection -

-

-

-

-

- + more
Respond
Tickets, alerts and your SIEM
-

-

-

-

-

- + more
Catch Issues Before They Reach the Repo
Code SAST Secure meets developers and coding agents where they work. The agent gets findings and fixes through the MCP server. The developer gets a pre-commit check from the command line interface (CLI). Then every pull request (PR) and build is checked again in the pipeline.
- Findings and fixes inside Claude Code, Cursor, GitHub Copilot and VS Code, through the MCP server
- A pre-commit hook that stops the issue before it is committed
- Pull request and pipeline checks, including malicious merge detection
- A software bill of materials (SBOM), AI BOM and SBOM diff for every build, plus AI Governance for the agents and SKILL.md files in your repos
 Code SAST Secure
 AI Auto-Remediation


Test Every Build Before It Ships
This is where Data Theorem sits in your pipeline, between build and release. Every mobile build, every API and the code behind them are tested automatically, and the release is checked before it goes out. No manual step, and no one waiting on a scan.
- Mobile Secure tests each iOS and Android release, fully authenticated, with no jailbroken or rooted devices
- API Secure runs authenticated testing through your identity provider for BOLA, privilege escalation and custom checks
- AI Exploits connects findings across apps, APIs and code to find the chains an attacker would use
- SAST+ takes issues proven at runtime and traces them back to the exact line in the repo
- Before release: App Store blockers, privacy checks and compliance reports, including PCI DSS, OWASP, HIPAA, GDPR and CCPA
 payments-app 5.4.0 iOS and Android, from your pipeline
In the pipeline
 AI Exploits: 1 exploit chain proven Plaintext token, then BOLA, then data exposure
Monitor and Protect in Production
On the ops side, Data Theorem keeps watching after release, in the running app and at the API. When something is attacked, it is stopped where it happens, and the block holds until the fix ships.
- Mobile Protect blocks tampering, debugging and reverse engineering inside the app, and flags fraud by session
- API Secure matches runtime attacks to what testing already proved and tells your web application firewall (WAF) what to block
- AI Active Protection detects prompt injection, large language model (LLM) abuse and AI scraping at the API layer
- Cloud Secure covers the cloud infrastructure your apps and APIs run on
 Mobile Protect
 Cloud Secure
 In the app Mobile Protect
 At the API API Secure
 /v2/accounts
 AI Active Protection Prompt injection stopped at /v1/assistant
 In your cloud:
Cloud Secure watches posture and attack paths from app to API to
cloud.
Respond Where You and Your Developers Work
Every finding and every runtime event goes straight to the systems your teams already watch. Developers get the ticket with the proof. Security gets the alert. Your security operations center (SOC) gets the event. Nobody has to open another console to find out what happened.
- Tickets in Jira and ServiceNow, with the proof, the affected code and remediation guidance
- Alerts in Slack and Microsoft Teams, for findings from testing and blocks at runtime
- Events sent to your security information and event management (SIEM) tool, such as Splunk
- The same finding is linked everywhere, so developers, security and the SOC work from one record


 + more


The Paved Road Methodology
Five principles behind every stage above, so security is built into the engineering workflow without slowing the business down.
- Auto-Triage Every issue ranked across apps, APIs and cloud, so teams see what matters first
- Remediation Guidance and secure code examples with every finding
- SDK & OSS Third-party SDKs and open source libraries checked the same way
- Shadow APIs Every API your apps call, including the ones nobody documented
- Pre-Prod Validation Store and compliance checks before the release goes out
More continuous checks added daily.
With Data Theorem, we have continuous security testing in place for all of our apps in the app stores with security discovery and inspection across our modern APIs.
Go Deeper on DevSecOps
Put Security in Every Stage
Start with one pipeline. See where Data Theorem fits, what it finds between build and release and how it protects what is already running.
- A scoped proof of concept Run on your own app, API or repo, time-boxed and agreed up front.
- Plugs into your pipeline Connect the CI/CD, repo and ticketing tools you already run.
- Results in your own tools Tickets, alerts and SIEM events from day one, in the systems your teams already use.