 AI Exploits
Every finding, weighed as part of a chain.
Links findings across your client, APIs and cloud into the path an attacker would take, with no source code required, so you fix what leads to your data first.
See AI ExploitsAPI Secure discovers every REST, GraphQL, gRPC, SOAP and serverless API, including the ones nobody inventoried. AI Exploits chains findings into the path an attacker would take, and runtime protection blocks attacks in production while the fix ships.
 AI Exploits: chain found
 GraphQL
 SOAP


Discovery, posture, testing and runtime protection run on the same engine, so every finding is connected.
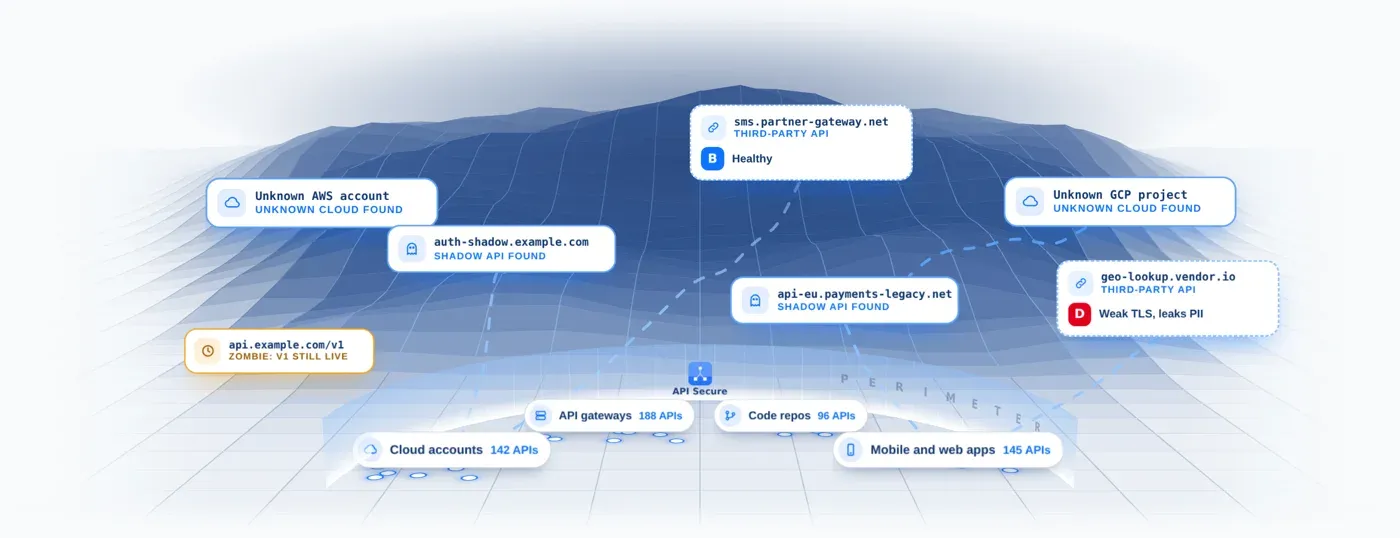
API Secure takes in every known source, from cloud accounts and gateways to code repositories. Then it works from the outside in, reverse engineering your mobile and web apps and probing your perimeter to find the APIs they actually call, including ones that point to clouds nobody knew existed.
"API Secure continuously discovers new and unmanaged APIs across our environment and inserts them into our SOR (System of Record), giving us confidence that nothing slips through the cracks."

Security Operations
Wells Fargo
API Secure scores every operation on its own across authentication, authorization, encryption and open security issues, then rolls those scores up into one grade for your whole API landscape.
It plays through your whole landscape, then a few individual APIs, so you can see exactly where each one lands.
API Secure watches how posture changes with every release. When a new release leaves a protected API unprotected, it is flagged as a Leaky API and your team is alerted right away.
API Secure tests your APIs both unauthenticated and authenticated. From the outside it probes your public APIs like an attacker would. Inside your environment, a scanner signs in with credentials re-provisioned from your identity provider, so authenticated tests like BOLA and privilege escalation keep running on their own.
API Secure and Cloud Secure see every layer of your stack. AI Exploits connects findings across your client, your APIs and your cloud infrastructure into the path an attacker would take to your data.
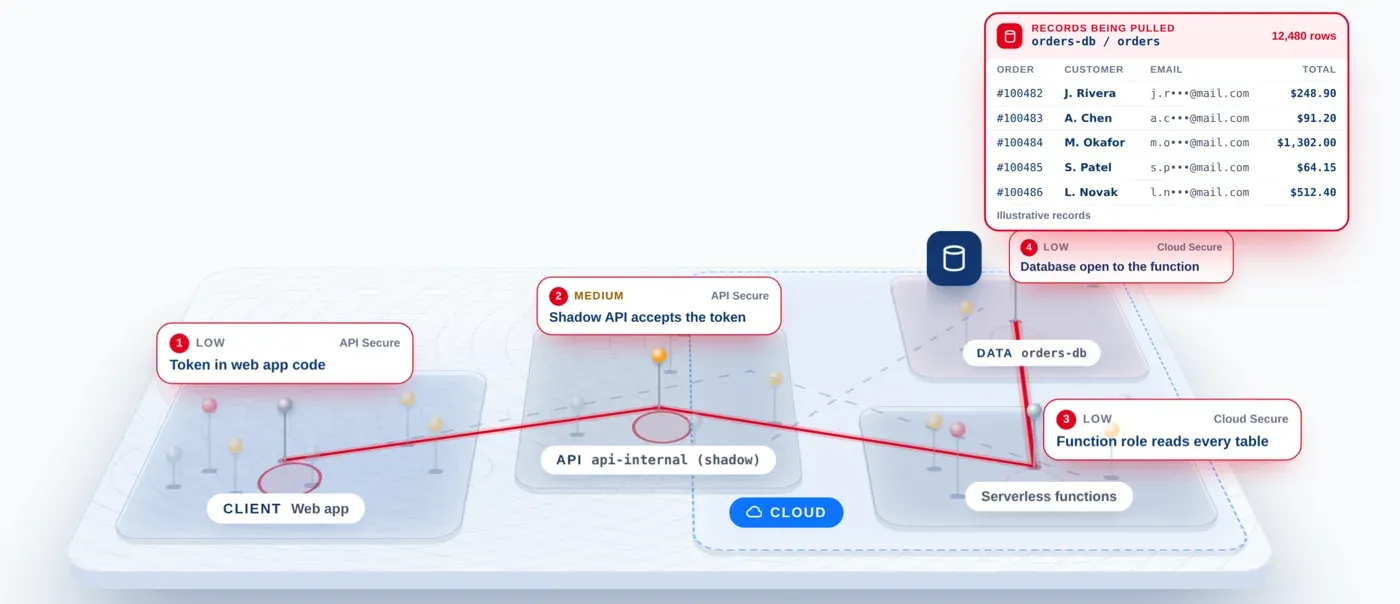
 Each finding looks minor on its own. AI Exploits shows how they line
up from client to cloud.
The same AI that maps the attack path also helps close it. Both come with API Secure.
AI Exploits Links findings across your client, APIs and cloud into the path an attacker would take, with no source code required, so you fix what leads to your data first.
See AI ExploitsWhen the API's code lives in a repository connected to Code SAST Secure, AI Auto-Remediation traces the finding that breaks the chain to its line of code and proposes the patch.
API Secure watches every API call in production, spots attacks, abuse and AI-driven threats, and has the WAF you already run block them. It also watches for APIs that start leaking data, and for attacks aimed at the AI models behind your APIs.
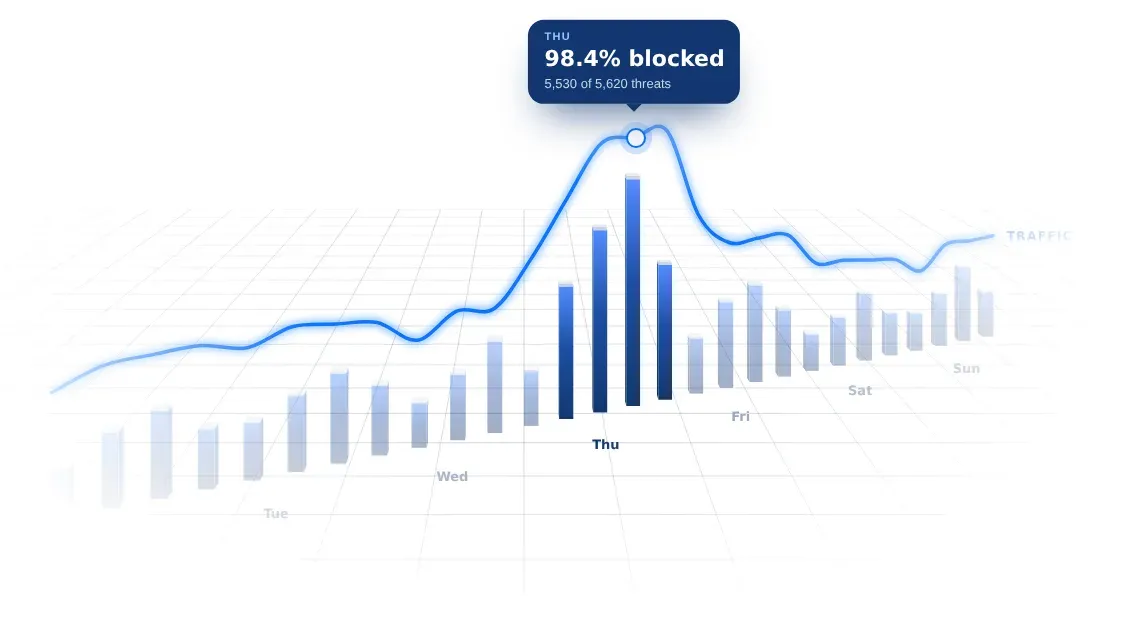
Every API call, seen in production from ALB logs and network taps.
Spots abusive, anomalous and fraudulent behavior as it happens.
Stops credential stuffing, password spraying and bot-driven account takeover.
Prompt injection, LLM abuse and AI-driven scraping.
SQL injection, XSS and SSRF caught in production.
Detections flow to your SIEM, ticketing and chat tools.
Tested in the pipeline, blocked at the edge, forwarded to the SIEM and ticketed in Jira, ServiceNow, Slack or Microsoft Teams, without anyone opening a new console.
Scored highest for API Security, in both the product and the service scores. 1
Read the Report : 2025 Gartner® Critical Capabilities for Application Security TestingNamed a leader in API security and management.
Read the Report : Leadership Compass: API Security and ManagementResearch report and customer survey on the state of API security.
Read the Report : Securing the API Attack SurfaceFind out how many APIs you really run, and which of them an attacker could chain into a breach.
Our team will reach out soon to schedule your personalized demo.
We’re looking forward to showing you what Data Theorem can do.
1 Gartner, Critical Capabilities for Application Security Testing, Mark Horvath, Jason Gross, Aaron Lord, Shailendra Upadhyay, 13 October 2025.
Gartner is a registered trademark and service mark, and Magic Quadrant is a registered trademark of Gartner, Inc.
Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
The Gartner document is available upon request from Data Theorem.