
Build at AI Speed. Stay Protected While You Fix.
AI lets your team ship a mobile app in hours. It also ships flaws nobody meant to write. Mobile Protect defends the app at runtime until those fixes land.
 Explore Mobile Protect
What AI Ships Without Telling You
Copilots, prompts and low-code tools write for speed, not secure design, and skip the reviews that would catch these flaws. Here are the ones that show up most, and what Mobile Protect does about each.
Hardcoded API keys and secrets in generated code
AI often drops a live production key straight into a class, with no secure config behind it.
Dynamic obfuscation changes the code every session, and decompile attempts are blocked in the app, so the key is far harder to pull out.
Move the key server-side and rotate it.
 Blocked by Mobile Protect Blocked in the app. Held until the fix ships.
You Ship in Hours. Fixes Take Longer.
The fix for a flaw nobody saw still moves through review, release, app store approval and user updates. Mobile Protect holds the line the whole way.
 With Mobile Protect Protected for 0 days
How Mobile Protect Secures Vibe-Coded Apps
Whether an app took an afternoon or a year, the same runtime defenses run inside it.
App Hardening
Anti-tampering, anti-debugging, root and jailbreak detection and emulator detection, running inside your iOS and Android apps.
Dynamic Obfuscation
Data Theorem dynamic obfuscation changes the code every session, so secrets and logic are far harder to lift from the binary.
 AI-aware
Real-Time Threat Detection
Overlays, malware injection, hooking frameworks and reverse engineering, including AI-assisted decompiling, are detected the moment they start. Tampering and decompile attempts are blocked in the app.
SSL Pinning
Built on TrustKit, Data Theorem's open source pinning library. Man-in-the-middle attempts are blocked and reported.
Fraud and Session Signals
Every session gets a fraud risk score from signals like rooted devices, cloned apps, automation and impossible travel. Likely fraud is flagged to your team, and you decide what to block.
Third-Party Code Firewall
Limits what embedded SDK code can do at runtime, so a risky dependency pulled in during prototyping has less room to cause harm.
 All of this ships in one SDK inside your iOS and Android apps.
Explore Mobile Protect
Then Fix It at the Source.
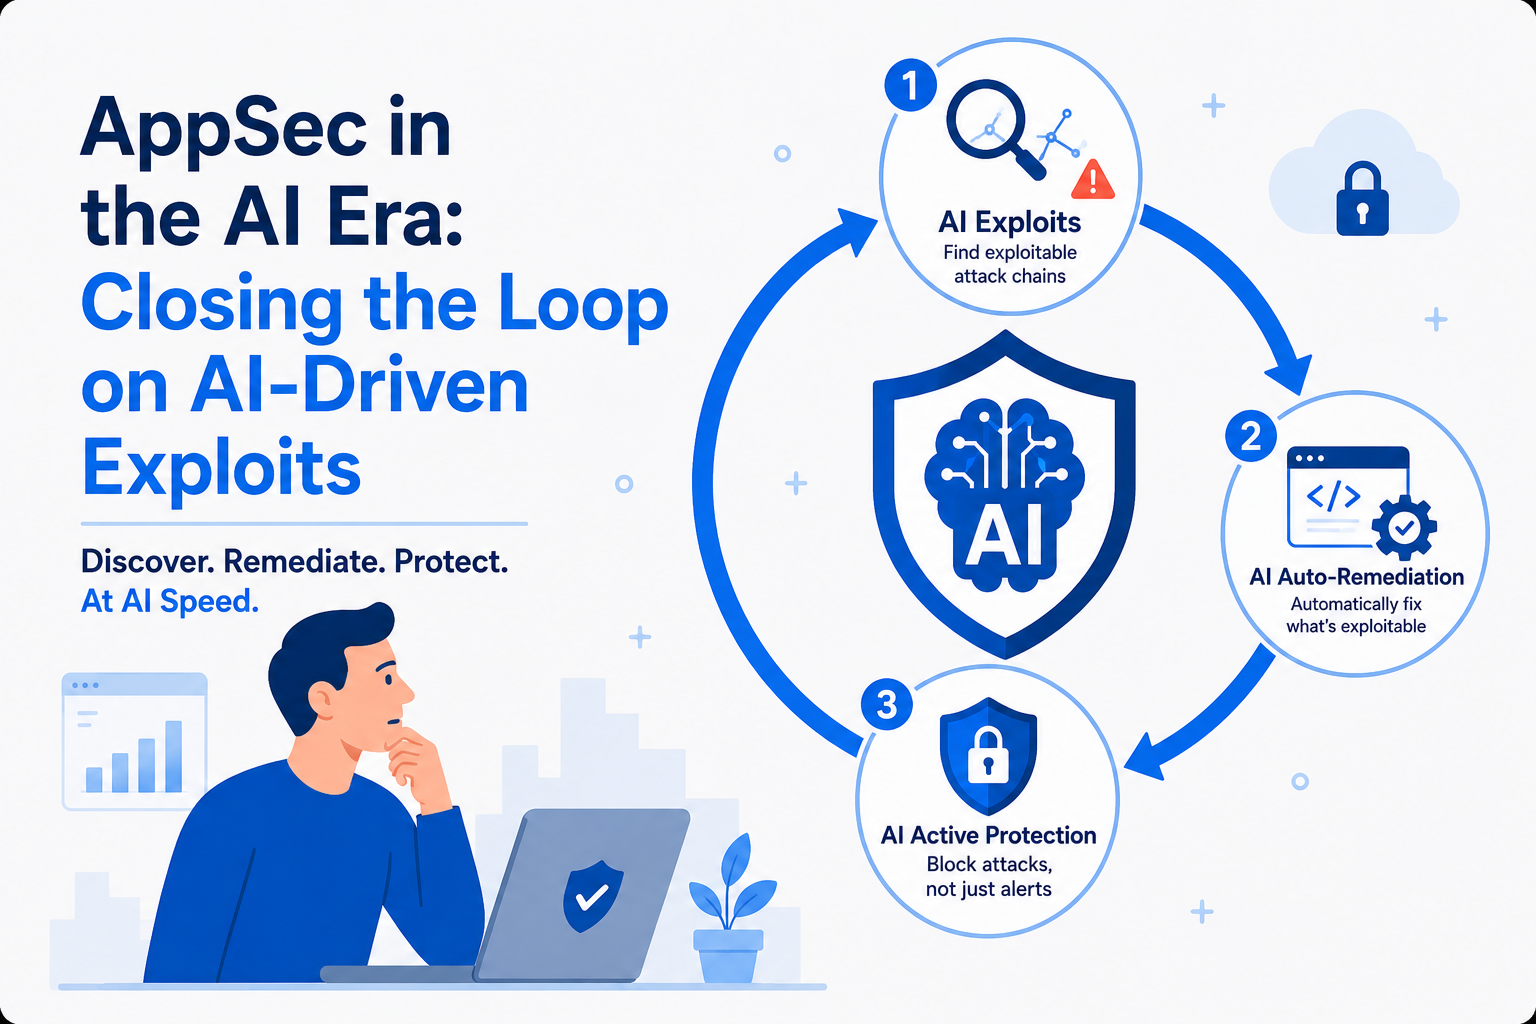
Mobile Protect buys your team time. These two close the gap for good.
 In every build Mobile Secure
Automated security testing for every mobile build you ship.
- Fully automated, with no jailbroken devices required
- Finds hardcoded secrets, insecure storage and weak TLS
- Flags vulnerable SDKs in each release
 In the repo Code SAST Secure
Catches the same flaws in code, for developers and coding agents alike.
- CLI pre-commit hook stops flaws before they are committed
- MCP server works inside your coding agent
- AI Auto-Remediation writes the fix
Research and Resources
Build Fast. Stay Protected.
See Mobile Protect running inside your own vibe-coded app.
Get Started