The Cloud Behind Every API and App, Secured.
Cloud Secure extends Data Theorem into the cloud services your APIs and apps run on. It inventories them, monitors their posture, hacks them before attackers do and protects cloud-native APIs at runtime, across AWS, Azure, GCP and private cloud.
Data Theorem ranked #1 in the Cloud Native Apps use case.1
Your Cloud Is Now Part of Your App's Attack Path.
Attacks start at the client and move through your APIs. Behind those APIs sit the managed databases, storage and serverless functions your apps are built on. Misconfigure one, and it becomes the last step of the attack.
Know Every Asset. Watch Every Posture Change.
Powered by the Data Theorem Analyzer Engine, Cloud Secure continuously discovers and inventories the cloud assets behind your APIs and apps: containers, databases, storage, serverless functions and secrets management. It checks posture across CSPM, KSPM and CIEM, secures containers down to the images in your cloud registries, and scans infrastructure as code with the same engine as Code SAST Secure. Findings reach your teams through dashboards and alerts, checked against compliance and audit policies.
- CSPM
- KSPM
- CIEM
- Continuous asset discovery
- Container and registry image security
- IaC scanning
- Compliance and audit policies
- APIs
- Containers
- Databases
- Storage
- Serverless
- Secrets
- CSPM Database accepts any function in the network orders-db · GCP Critical
- CIEM Function role can read every table payment-handler · Azure High
- KSPM Pods run as root prod-api-cluster · AWS High
- IaC Storage account logging disabled payments-storage · Azure Medium
- Image Registry image with a known CVE registry/api-internal:2.4 · AWS Medium
Hack Your Own Cloud First.
Hacker Toolkits run automated red-team and penetration testing exercises across the attack surfaces in your cloud-native application stack, with daily updates on the vulnerabilities and exploits that lead to external attacks and data breaches. Hacking your own cloud is attack surface management that lowers the odds of a preventable breach.
-
Automated red-team exercises
Pen-testing across the cloud-native stack without scheduling a team. -
Daily exploit updates
New vulnerabilities and exploits, checked against your clouds every day. -
Attack path visualization
See how a weakness in one layer leads to data in another.
Protect the APIs Running in Your Cloud.
Data Theorem SDK libraries add real-time telemetry and policy-based blocking to your cloud-native APIs and applications. Teams see attacks as they happen and fix problems faster, in every cloud you run.
- Real-time telemetry Runtime observability for the APIs and functions you run in the cloud.
- Policy-based blocking Stop requests that break policy before they reach your data.
- Built for cloud-native apps Protection for serverless and API services across clouds.
- Telemetry
- Streaming
- Policy
- Block mode
- Cloud
- Azure
- 14:02:11 POST /payments Valid session Allowed
- 14:02:12 POST /payments Injection pattern in request body Blocked
- 14:02:14 GET /payments/{id} Valid session Allowed
- 14:02:15 GET /payments/{id} Enumeration across account IDs Blocked
Findings Land Where Teams Already Work.
Connect your clouds once. Posture findings, toolkit results and runtime events are ticketed, alerted and forwarded to the SIEM without anyone opening a new console.









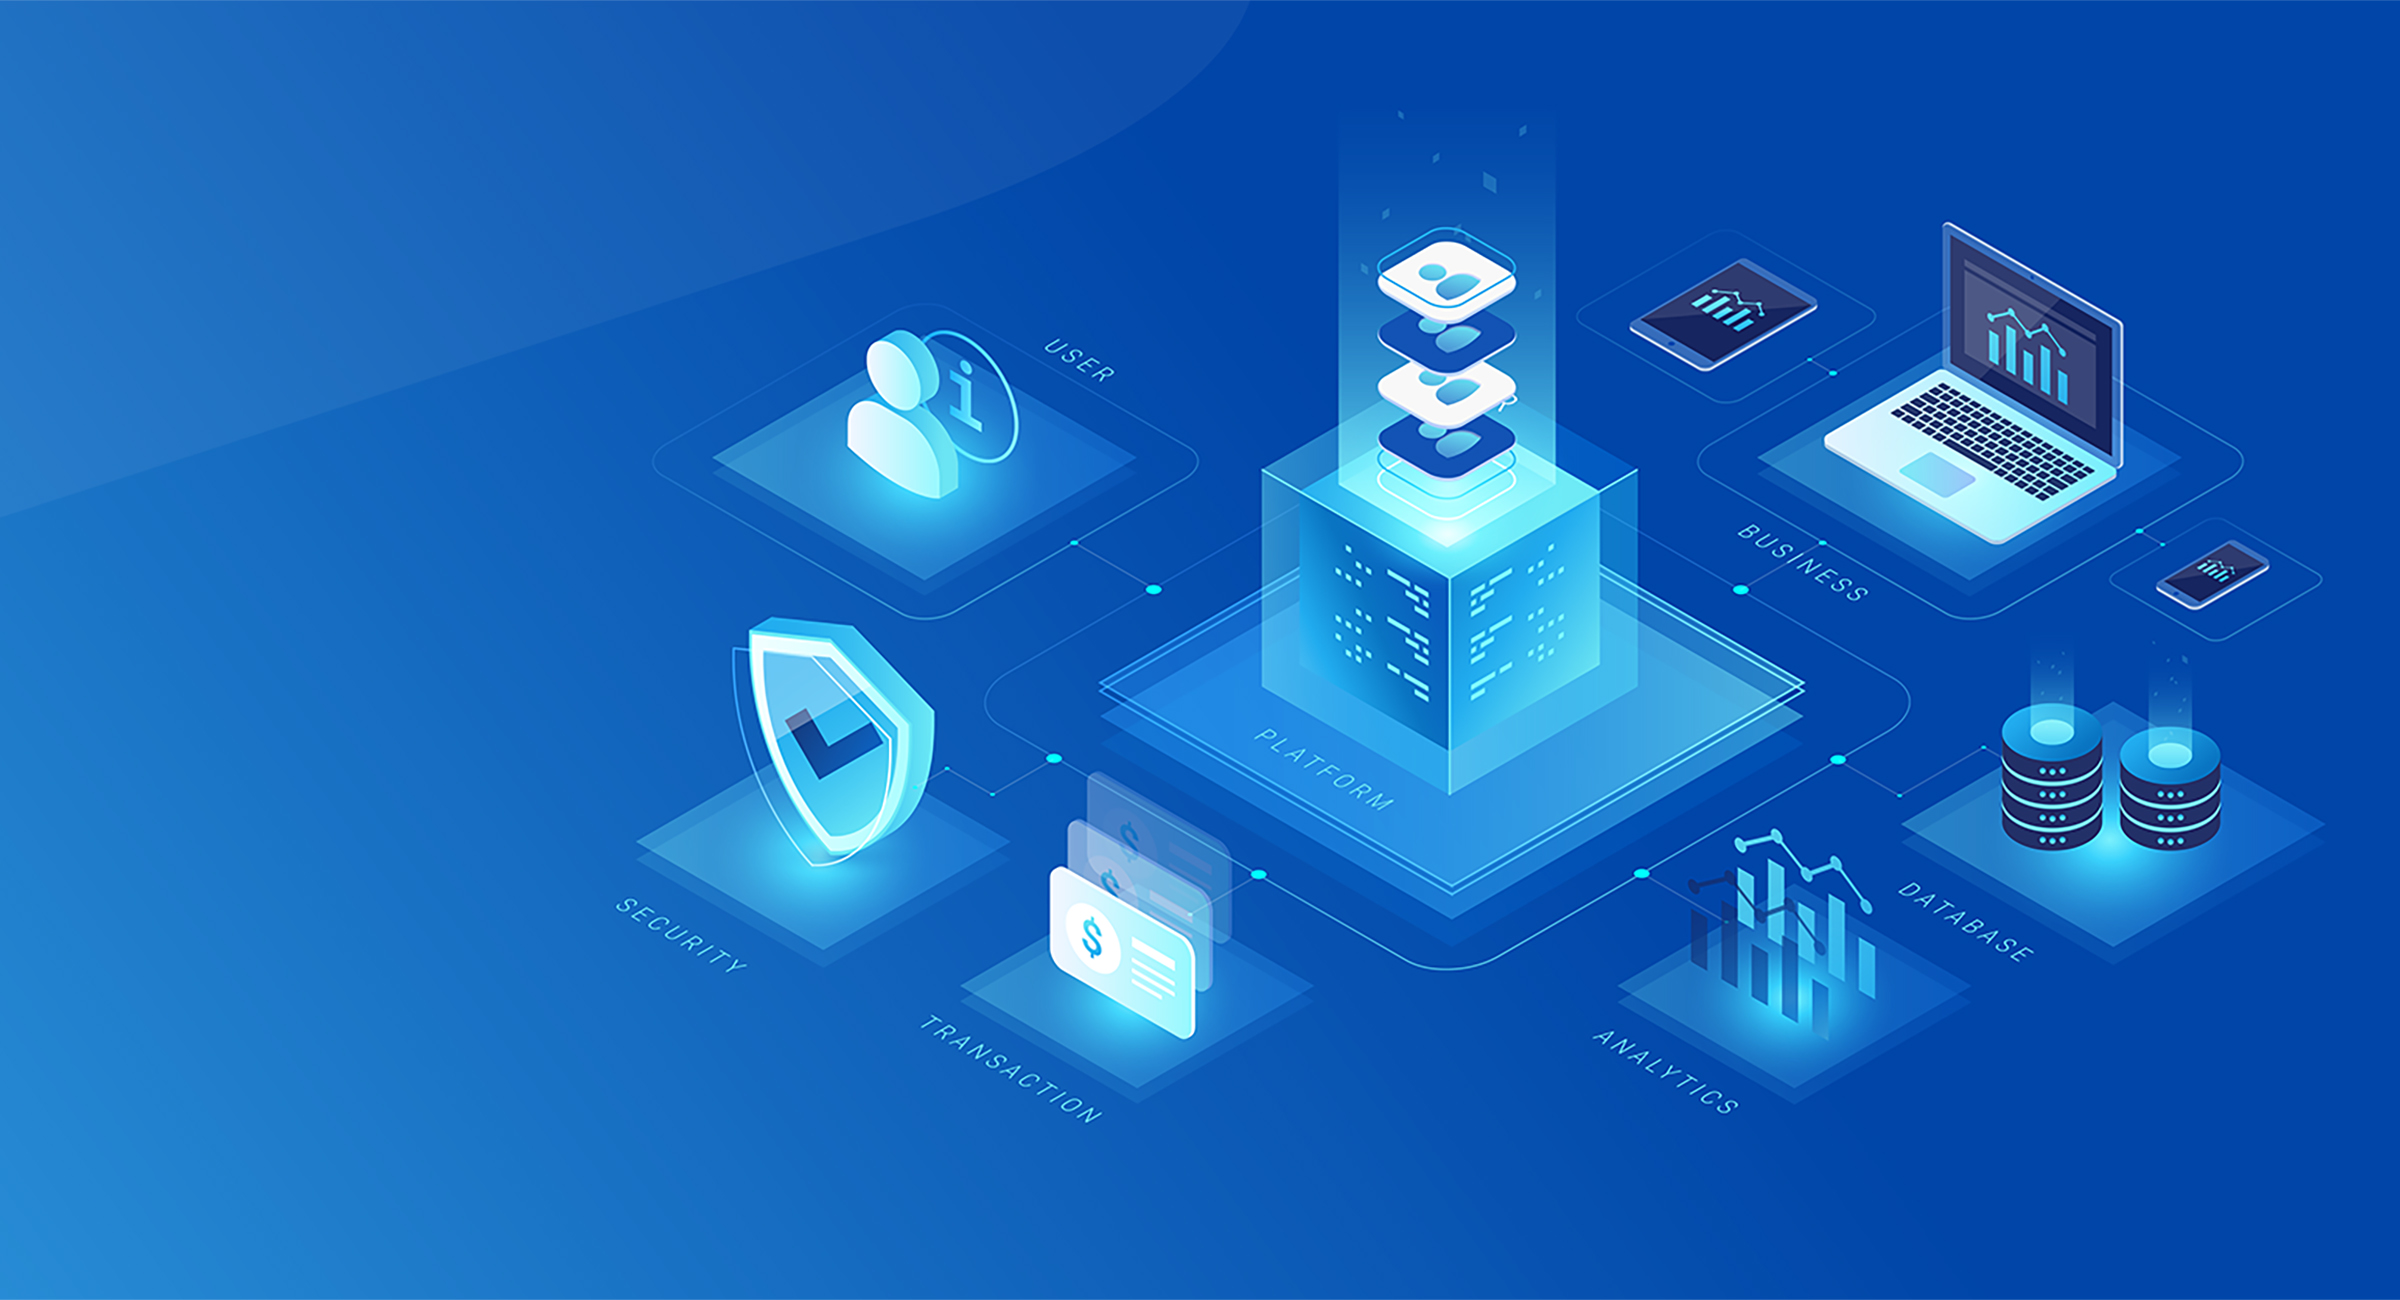
The Cloud Beneath Every App.
Your apps call APIs, and those APIs run on cloud services. API Secure discovers, tests and protects the APIs. Cloud Secure covers the resources, roles and data behind them.
Code SAST Secure catches infrastructure as code misconfigurations in the repository, before they ship. Cloud Secure runs the same IaC checks on what is deployed, and secures the containers and registry images your APIs and apps run on.
Research and Resources
See Cloud Secure in Action
Find out what is really running in your clouds, and which of it an attacker could reach through your apps.
Thank you. We’ve received your request.
Our team will reach out soon to schedule your personalized demo.
We’re looking forward to showing you what Data Theorem can do.
1 Gartner, Critical Capabilities for Application Security Testing, Mark Horvath, Jason Gross, Aaron Lord, Shailendra Upadhyay, 13 October 2025.
Gartner is a registered trademark and service mark, and Magic Quadrant is a registered trademark of Gartner, Inc.
Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
The Gartner document is available upon request from Data Theorem.