AI-Driven Application Security
Prevent AppSec Data Breaches in the AI Era
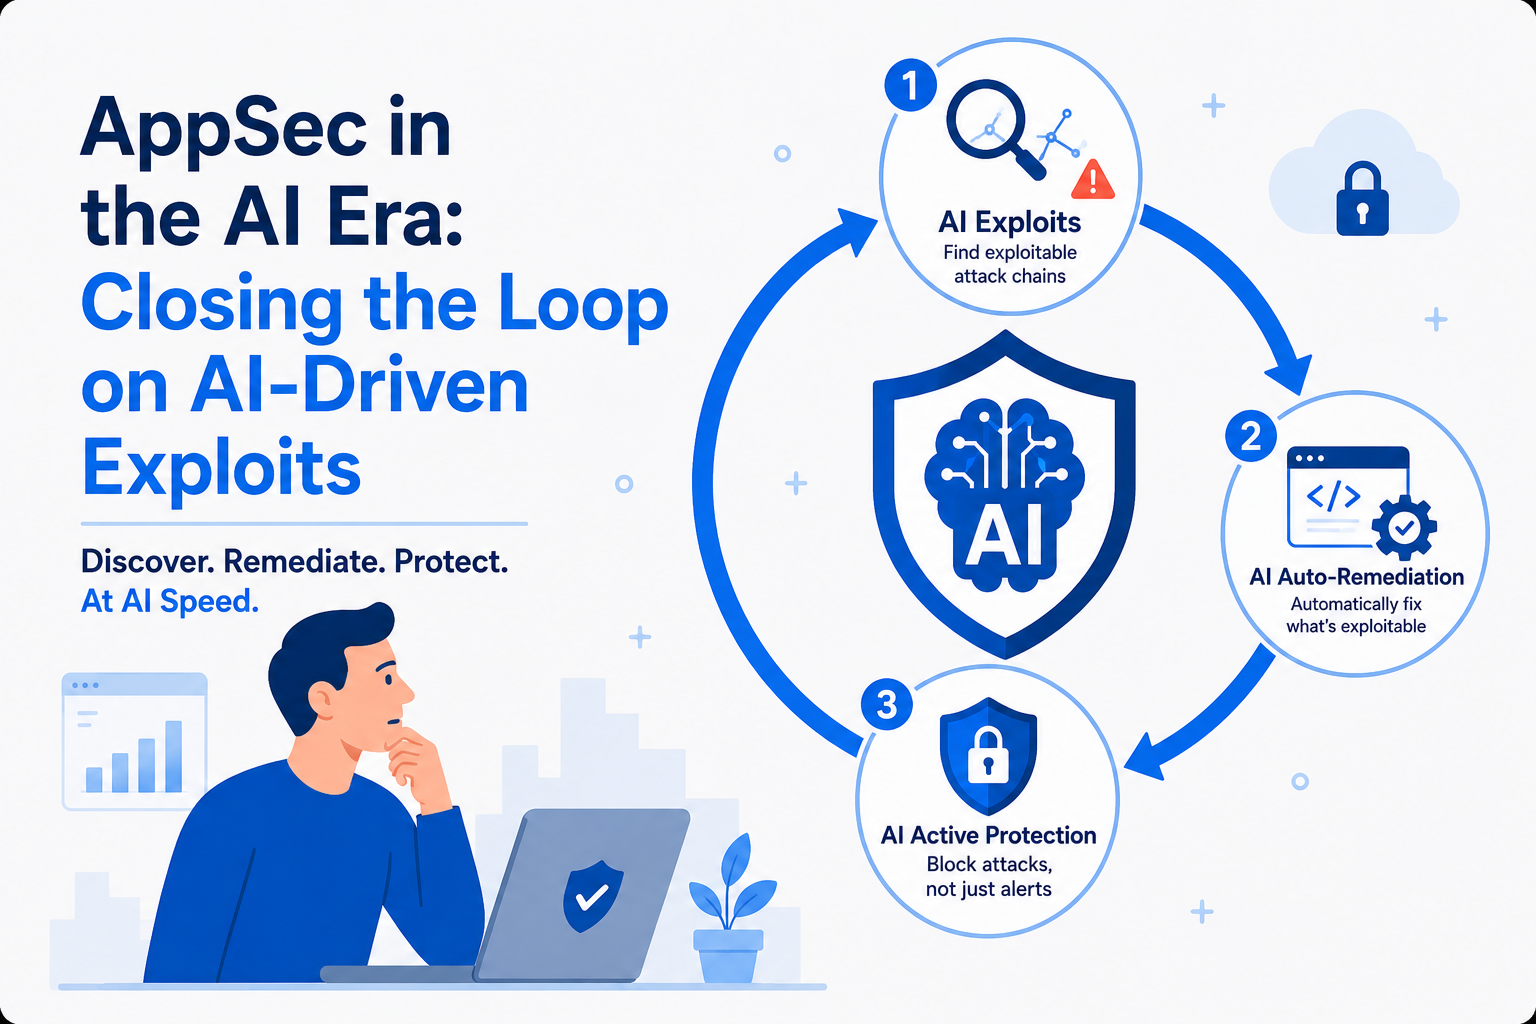
Attackers now use AI to find and chain exploits across your apps and APIs. Data Theorem uses AI to find those chains first, fix them in code and block them at runtime, on one platform from code to cloud.
 AI agent · Tokyo


 AI-enabled attacker
 Data Theorem response


The Mission, Now With AI
Preventing AppSec Data Breaches Has Always Been the Mission. AI Changes the Game.
Since 2013, Data Theorem has had one focus: preventing AppSec data breaches across your apps, your APIs and the cloud behind them.
AI changes the game. Attackers use it to decompile apps, map APIs and chain small issues into a breach faster than any team can triage.
The only way to keep up is to use AI to stop AI, at every point an attacker would reach for.
Using AI to stop AI means three things

The New Reality
AI Attackers Chain the Lows. It Takes AI to Stop AI.
AI tools let attackers decompile apps, map APIs and line up small issues into a path to your data. Point tools grade every issue on its own. AI Exploits reads the whole field and finds the chain first.
One Platform
Every Layer of the Application, One Platform
Data Theorem covers the code, the running apps and APIs, and the runtime they live in. Every finding is checked against the others, so you fix what an attacker can actually reach.
 Mobile Secure
 API Secure
 Mobile Protect
 AI across every layer
 AI Exploits AI Auto-Remediation AI Active Protection

From code to cloud. Cloud Secure extends the view to the cloud infrastructure your apps and APIs connect to and run on.
Explore Cloud SecureUnderstand · Dynamic Testing
Test Like an Attacker, Fully Authenticated
Most attacks happen after login. Mobile Secure and API Secure test your running apps and APIs signed in, and SAST+ traces every verified finding back to the line of code.
Signed In From the Moment the App Launches
The scan opens the app, signs in and follows it screen to screen, like a real user and a real attacker.
Testing That Logs In, the Way Attackers Do
Real sessions find the authorization flaws, like BOLA and privilege escalation, that unauthenticated scanners never reach.
Remediate · Code
Fix at the Pace AI Attacks Demand
When AI finds an issue, the fix has to keep up. Code SAST Secure scans your repos for vulnerable code, vulnerable open source and what is inside every build, and AI Auto-Remediation hands the fix to your coding agent before the commit.
- Static application security testing (SAST) and software composition analysis (SCA) in 20+ languages
- A software bill of materials (SBOM) and AI BOM for every build
- Findings and fixes inside your coding agent through the MCP server, and a pre-commit hook for developers
- AI Governance for the agents, AI-written code and SKILL.md files in your repos
 Code SAST Secure AI Auto-Remediation
Defend · Runtime
Runtime Is the First Layer of Defense
Finding the chain is step one. The fix still takes a release to ship. Here’s how runtime protection holds the line until it does.
-
Day 0 · Found
AI Exploits finds the chain
Validated before release. The fix goes into the next release.
-
Day 1 · Attack
An attacker tries it the next day
AI tooling decompiles the app, pulls the key and calls the API.
-
Day 1 · Blocked
Runtime breaks the chain
Mobile Protect stops the tampering. API Secure has your WAF block the call.
-
Day 6 · Fixed
The fix ships. The chain is closed.
AI Auto-Remediation wrote the patch. Runtime protection stays on.
 Exploit chain

 Runtime still watching
 AI Exploits, Powered by ARCANE
Think Like an AI Attacker. Defend at AI Speed.
ARCANE, Data Theorem’s AI exploit engine, proves every chain at runtime before it reaches you. See how AI Exploits, AI Auto-Remediation and AI Active Protection close the loop.
DevSecOps
Where Data Theorem Plugs In
Data Theorem was built in 2013 to run inside the release process, with no manual step in the loop. It remediates in the code, tests between build and release, and protects your apps and APIs in production, so AppSec scales with development instead of slowing it down.
Code
Issues fixed where developers and agents write code
-
 No bad commits Code SAST Secure
- Findings in the IDE and agent MCP server and CLI
 AI Auto-Remediation


Build
Repos and pipelines, checked on every pull request and build



 AI Governance


Security Testing
Every build tested in your pipeline
- Mobile apps Mobile Secure
- APIs API Secure
- Code Code SAST Secure
AI Exploits 
Release
Store submissions and every published app


Monitor
Apps and APIs monitored and protected in production
-
 In the app Mobile Protect
- At the API API Secure
-
 In the cloud Cloud Secure
AI Active Protection -

-

-

-

-

- + more
Respond
Tickets, alerts and your SIEM
-

-

-

-

-

- + more
With Data Theorem, we have continuous security testing in place for all of our apps in the app stores with security discovery and inspection across our modern APIs.
Resources
Go Deeper on AI-Driven AppSec
Get Started
Use AI to Stop AI
See how Data Theorem finds, fixes and blocks AI-driven exploits across your code, apps and APIs, in one closed loop.
- Your exploit chains, found first See what an AI attacker could chain across your own app and API.
- Protection while the fix ships Runtime blocking in the app and at the API from day one.
- Fits your pipeline Connects to the repos, CI/CD and ticketing tools you already run.