Why SAST Backlogs Keep Growing
SAST tools are good at finding issues. The hard part has always been what comes next. Each finding needs someone to confirm it is real, understand the code path, research the right fix and make the change without breaking anything. Multiply that by hundreds of findings across dozens of repositories and backlogs grow faster than teams can clear them.
AI coding agents now write a large share of new code, which adds volume and new kinds of risk. Security has to keep up at the same speed.
What Good AI Auto-Remediation Looks Like
- Prioritized first. Start with findings that are reachable and exploitable, not every theoretical issue.
- Precise guidance. The fix should be specific to the code, framework and library version in your repository.
- Delivered where developers work. In the IDE, through the coding agent, and in the pull request.
- Caught before the commit. Fixing at commit time is cheaper than fixing after release.
- Human in the loop when you want it. Teams should be able to require review or let fixes flow automatically.
- No new black box. Fixes should be transparent and reviewable like any other code change.
The Coding Agent Changes the Workflow
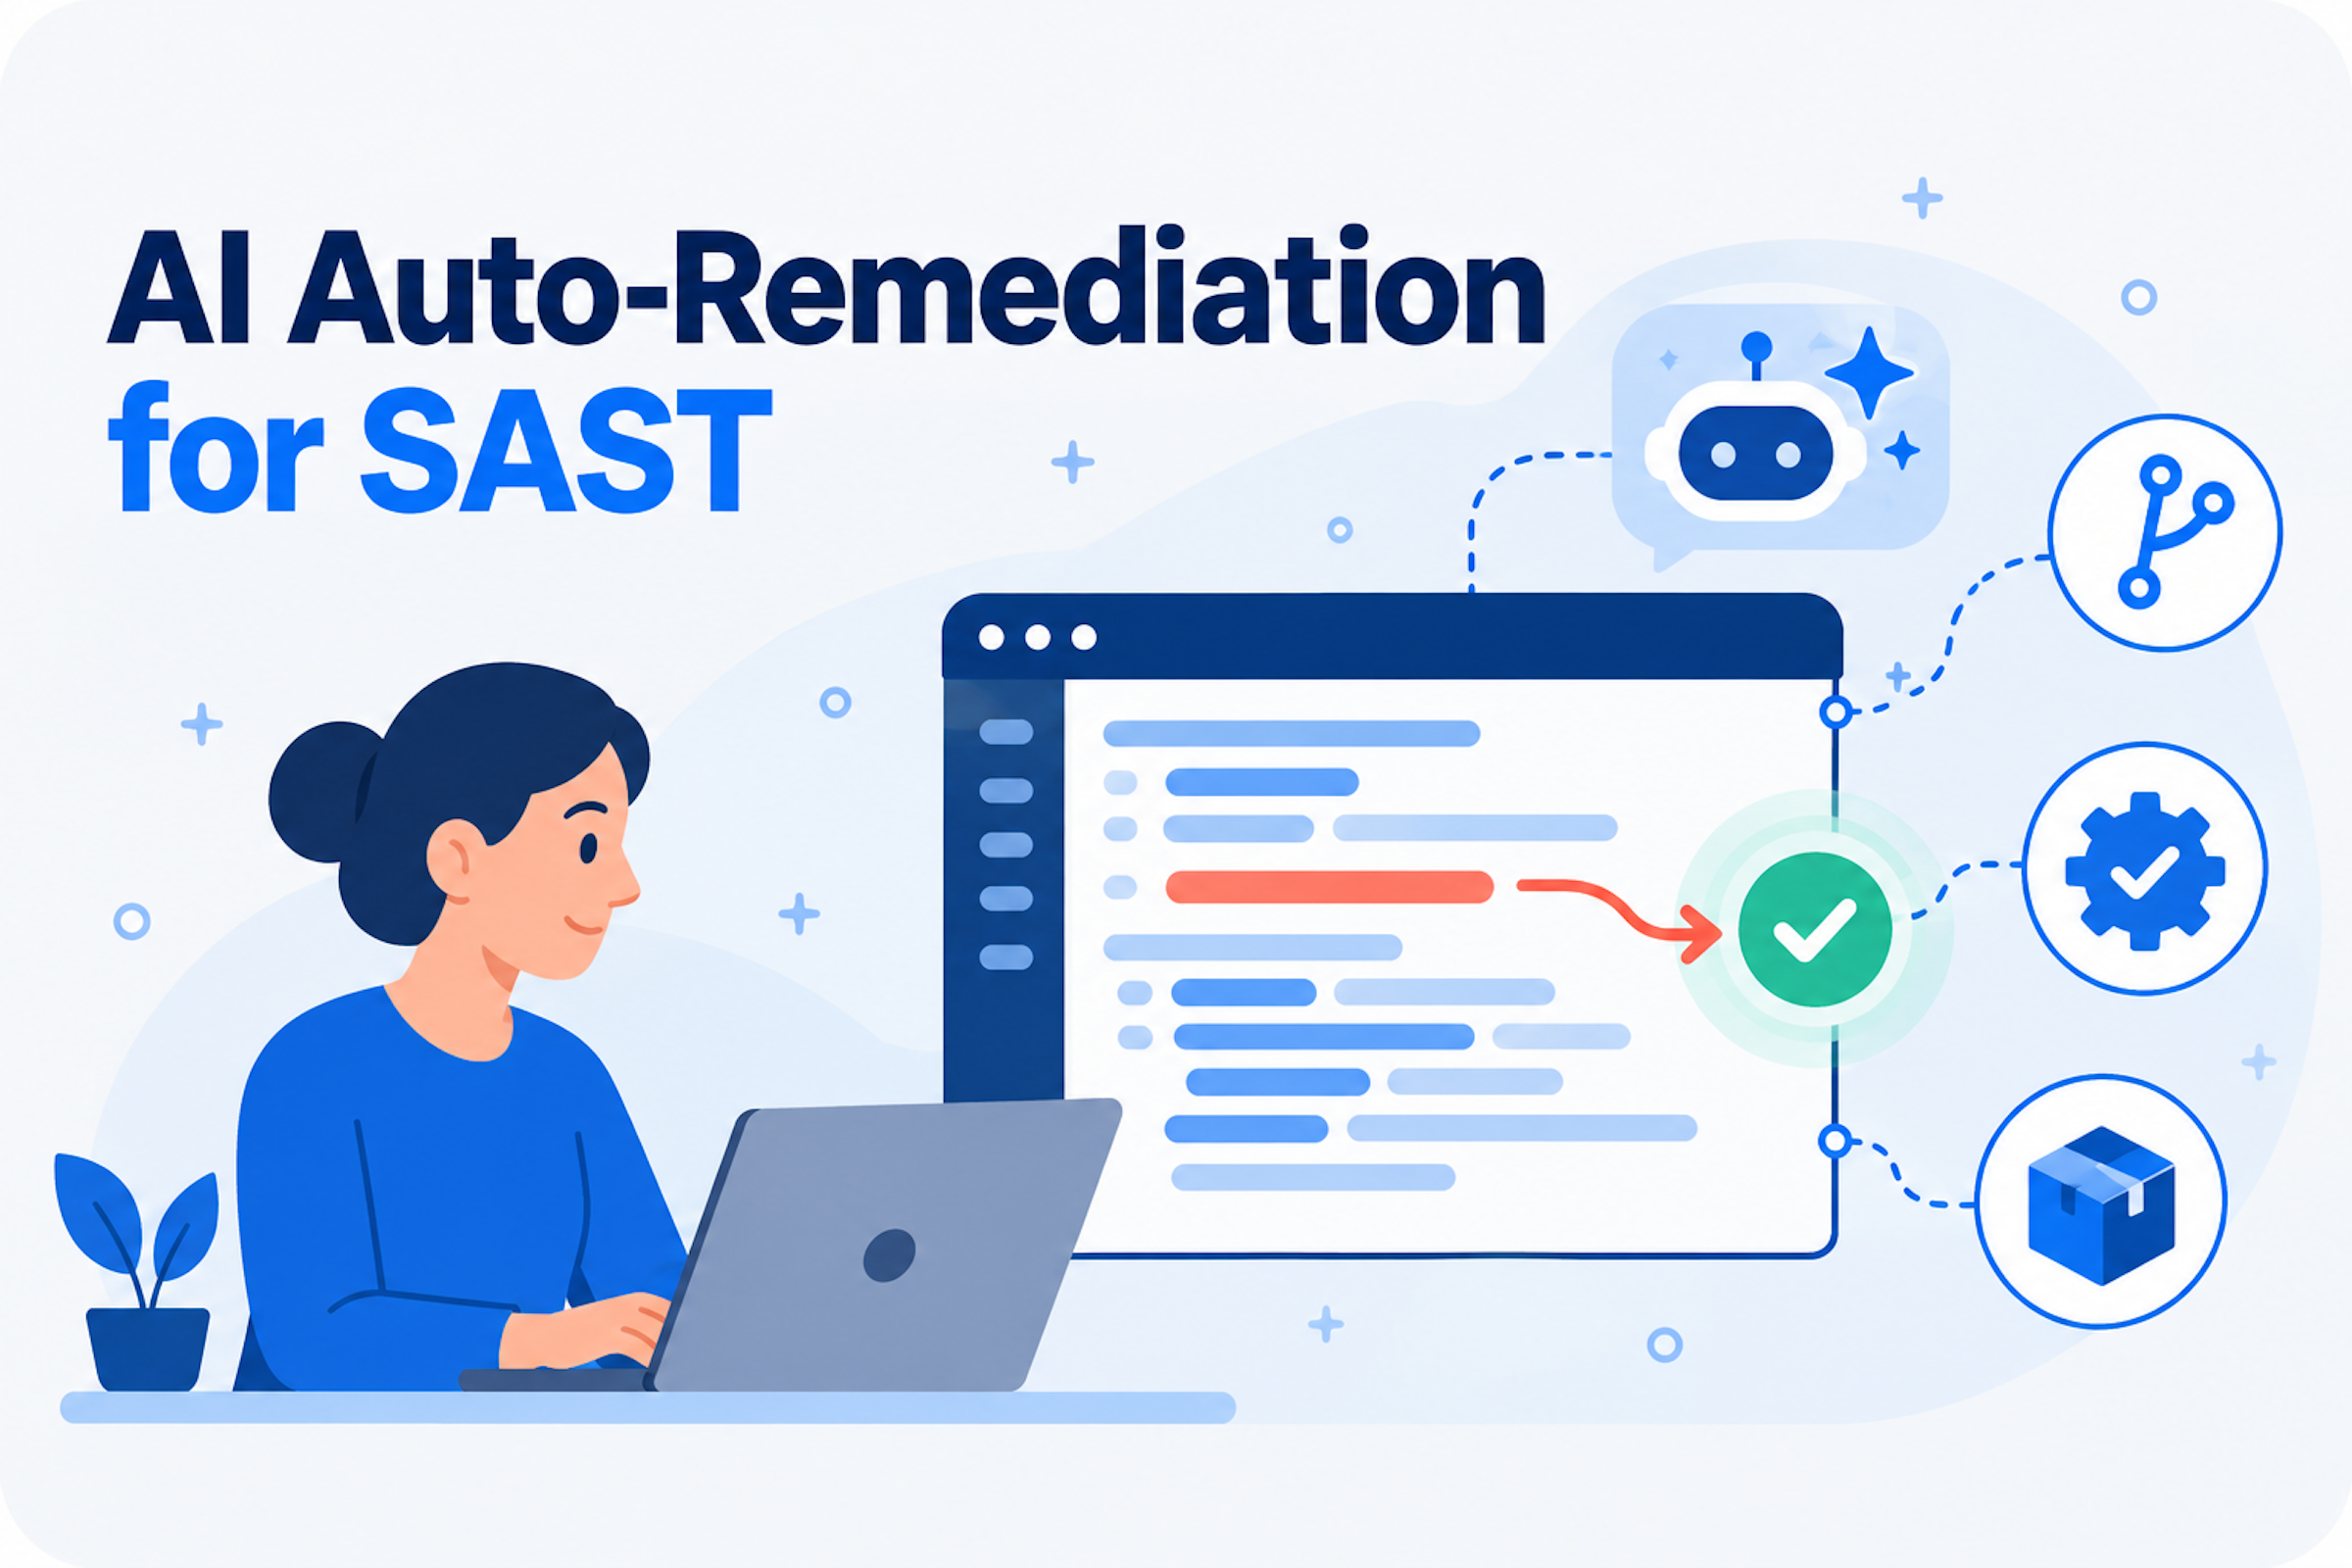
With AI coding agents in the IDE, remediation can move from "file a ticket" to "apply the fix now". The security platform's job is to give the agent exactly what it needs: the verified finding, the location, and optimized remediation guidance. When the guidance is precise, the agent skips the research, makes the correct change and uses fewer tokens to get there. A lower-cost model can often do the work.
How Data Theorem Code SAST Secure Does It
Code SAST Secure combines SAST, SCA and SBOM in one product and leads with AI Auto-Remediation through your own coding agent:
- Catches both the agent and the developer before commit.The Code SAST Secure MCP server works with coding agents in tools such as VS Code, Cursor, Claude Code and GitHub Copilot. A CLI pre-commit hook catches issues from developers before code is committed.
- Fixes that are optimized for your agent.Data Theorem supplies remediation guidance so your model implements the exact fix. You run your own approved models, so Data Theorem adds no variable model cost.
- Exploitability first.SAST+ correlates findings verified by Mobile Secure or API Secure dynamic testing back to the code, and Code Canary confirms reachability when a marker placed in the code trips at runtime.
- Full code coverage.20+ languages, SCA, SBOM, SBOM diff, VEX, vendor SBOM uploads, malicious merge detection and AI governance for the agents, AI-written code and SKILL.md files in your repositories.
- Deploy your way.Scan cloud Git platforms, or run the scanner entirely on-premises in your environment.
AI Auto-Remediation works with or without a human in the loop. If your team wants review, it still catches the issue and delivers the fix guidance for approval.
Code SAST SecureCombines SAST, SCA and SBOM in one product.Learn MoreRelated Data SheetCode SAST Secure Data SheetFind, fix, and remediate exploitable code vulnerabilities across first-party source, open source, and AI-generated code. Code SAST Secure is Data Theorem's developer-side application security platform: it scans source, bytecode, and compiled artifacts with SAST, verifies exploitability through DAST (SAST+), continuously inventories open-source dependencies and SDKs with SCA and SBOM, and auto-generates secure patches for actively exploitable open-source and AI-written code. Download the datasheet to see how find, fix, verify, and remediate come together in one platform.Read Now
Frequently Asked Questions
What Is AI Auto-Remediation?
Using AI to turn a security finding into a specific, working code fix that a developer or coding agent can apply.
Is AI Auto-Remediation Safe?
Fixes are code changes like any other: they go through your normal review, tests and pull requests. Teams can require human approval.
Does AI Auto-Remediation Work with SCA Findings?
Yes. Vulnerable dependencies can be upgraded or patched with guidance specific to your version.
Do I Need a Specific AI Model?
No. Code SAST Secure works with the coding agents and models your team already uses.