Inside the Data Sheet
What You Will Learn
-
Exploitable Bugs, Not Noise
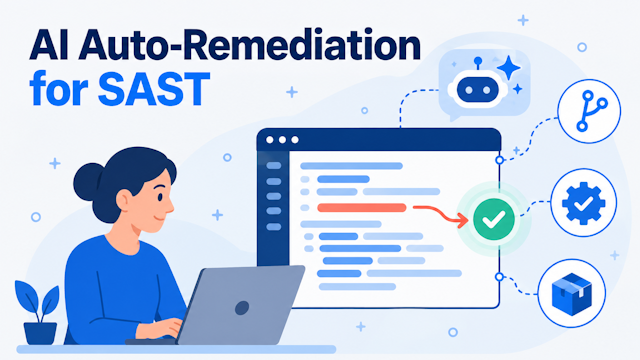
How SAST+ runs Data Theorem's dynamic testing against SAST findings, where available, to filter out dead code and false positives.
-
AI Code Patching
How Code SAST Secure generates secure fixes for actively exploitable open source and AI-written dependencies, closing the zero-day window.
-
Fixes Where Developers Work
How native IDE and CI/CD integration, including MCP support for AI-native IDEs, delivers context-aware patches across 20+ languages.
Frequently Asked Questions
What does Code SAST Secure cover?
SAST for first-party source, bytecode and compiled artifacts, plus SCA and SBOM for open source dependencies and SDKs.
What is SAST+?
Data Theorem's approach of checking SAST findings against dynamic testing, where available, so developers see exploitable issues first.
Does it fix AI-generated code?
Yes. It generates secure patches for actively exploitable open source and AI-written code.
Which frameworks does it map to?
The CWE Top 25 and the OWASP Top 10.
- CWE Top 25
- OWASP Top 10